Returnero Leaks 200,000 Government Records
A dark web forum breach exposing 200,000 citizen records has highlighted severe identity theft and social engineering risks across public administration databases. FemtoSec provides deep technical analysis of the exfiltration vectors, MITRE ATT&CK mapping, and actionable containment measures for security teams.
Key Takeaways
- A threat actor operating as Returnero claimed the leak of 200,000 public sector citizen records.
- Exposed fields include full names, national identity numbers (DNI), birth dates, and residential addresses.
- The data presents severe secondary risks, including targeted phishing, social engineering, and fraudulent financial onboarding.
- Defenders must isolate database ports, enforce least-privilege service roles, and audit web applications for API and SQL flaws.
Massive exposure of national identity documentation threatens regional citizen trust and opens immediate pathways for high-volume identity fraud and targeted social engineering. When 200,000 sensitive citizen profiles surfaced on illicit dark web channels, the operational impact extended far beyond the immediate provincial perimeter, creating widespread secondary credential stuffing and impersonation hazards across both municipal operations and regional financial services.
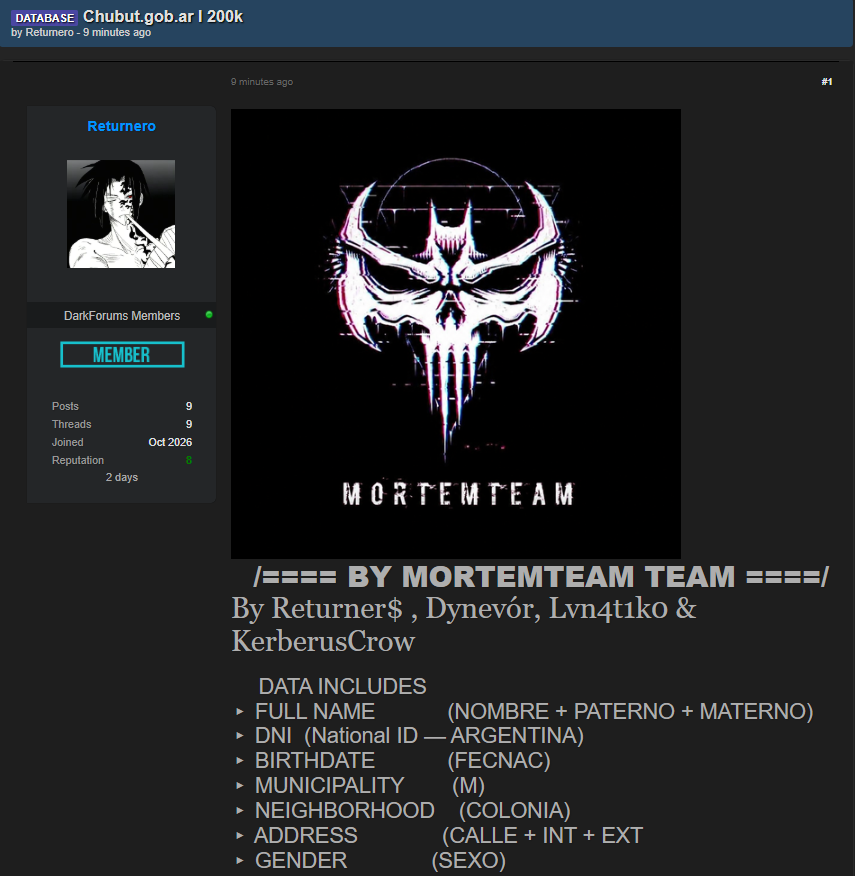
The exfiltrated database, attributed to a threat actor operating under the handle Returnero, was published on underground cybercrime forums alongside similar municipal datasets. Public administration networks hold authoritative citizen registries, making them high-priority targets for financially motivated breach actors seeking to commercialize personal identifiable information (PII) or fuel broader credential-harvesting campaigns.
Returnero Exfiltration Scale
What Was Exposed
The compromised dataset contains 200,000 detailed records originating from the public sector domain chubut.gob.ar. Analysis of the exfiltrated records indicates an aggregate citizen census, electoral registry, or municipal assistance database containing highly granular personal information.
The exposed data fields cataloged in the dark web archive include:
Full Legal Names: Complete individual identifiers representing residents and provincial personnel.
National Identity Document Numbers: Official DNI (Documento Nacional de Identidad) numbers, which serve as foundational identifiers for Argentine civil, financial, and digital government interactions.
Dates of Birth: Precise demographic data required for secondary identity verification and password recovery mechanisms.
Residential Geolocation Data: Detailed municipal affiliations, neighborhood designations, and residential street addresses.
Gender Identifiers: Demographic tracking attributes cross-referenced with official civic entries.
The combination of unchanging identity document numbers with verified physical addresses creates an acute vector for impersonation. Threat actors routinely leverage such authoritative tables to bypass knowledge-based authentication (KBA) protocols used by regional banking, credit-scoring, and telecommunications providers.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Compromised Citizen PII Blast Radius
- DNI & Identity Fraudhigh
- KBA Verification Bypasshigh
- Targeted Phishing & Vishinghigh
- Financial Account Takeoverhigh
- Downstream Enterprise Whalingmedium
How the Data Got Out: Technical Attack Analysis
While provincial administrative authorities have not issued a post-mortem incident report confirming the precise root cause, the structural layout of the leaked records and typical threat actor tradecraft highlight clear initial access and exfiltration vectors. The threat actor, Returnero, has targeted multiple regional government entities across Latin America in coordinated dark web dump releases.
Probable Attack Vectors
Security practitioners evaluating this threat landscape should analyze three high-probability entry points:
Web Application Exploitation (T1190): Public-facing civic verification portals and municipal service web applications often connect directly to backend relational databases. Unauthenticated SQL injection (SQLi) vulnerabilities in query forms or broken object-level authorization (BOLA) flaws within citizen lookup APIs provide direct avenues for automated bulk database extraction.
Compromised Administrative Credentials (T1078): Infostealer malware families (such as Lumma, RedLine, and Vidar) frequently harvest active session cookies and cleartext credentials from administrative workstations. Leaked VPN, remote desktop, or database management interface credentials (e.g., phpMyAdmin or pgAdmin) facilitate immediate, legitimate-appearing access to internal environments.
Exposed Storage and Misconfigured Backups (T1213): Administrative backup scripts frequently dump raw database snapshots (such as
.sql,.csv, or.dumpfiles) to staging servers. If these archives are written to world-readable directories or misconfigured object storage buckets, threat actors can download them without triggering complex database alarms.
MITRE ATT&CK Technical Mapping
The attack chain exhibits classic stages of opportunistic database extraction and monetization:
Initial Access (T1190 / T1078): Exploitation of exposed public web services or usage of valid accounts gathered via dark web markets.
Discovery (T1083 / T1497): Enumeration of backend database tables and administrative access tiers.
Collection (T1005 / T1213): Automated bulk extraction of civic tables utilizing native export commands (e.g.,
mysqldump,pg_dump) or scheduled API queries.Exfiltration (T1048): Exfiltration over alternative protocols, transferring compressed relational archives to external command-and-control (C2) or file-sharing nodes.
Impact (T1491.001): Public publication of data archives on illicit breach forums to generate illicit reputation or financial gain.
Downstream Risk
The downstream consequences of public sector data leaks unfold over several months. Because national identity numbers cannot be easily reissued like passwords or credit cards, the long-term attack surface for exposed citizens remains elevated indefinitely.
Critical follow-on risks include:
Targeted Spear Phishing and Voice Phishing: Fraudsters weaponize validated names, DNI numbers, and home addresses to craft convincing social engineering lures. Citizens and government staff may receive communications purporting to originate from tax agencies, utility providers, or provincial ministries requesting secondary credential confirmation.
Financial Account Takeover: In many jurisdictions, financial institutions, micro-lenders, and fintech platforms rely on government-issued identity cards and birth dates for customer onboarding or account reset workflows. Attackers exploit these compromised data points to establish fraudulent credit lines or bypass telephone banking verification.
Secondary Organizational Infiltration: If government employees or municipal contractors are included within the census leak, attackers can cross-reference physical addresses and personal details against corporate directory data. This enables bespoke whaling campaigns designed to breach downstream enterprise supply chains.
Organizations operating in regions affected by such disclosures should implement continuous Dark Web Monitoring to track credential spillover and alert administrators before compromised identity signals lead to corporate perimeter compromises.
Recommended Defense-in-Depth Controls
- L1Edge & Web ApplicationWAF inspection for SQL injection syntax (UNION SELECT, SLEEP)Strict parameter binding and rate limiting on citizen lookup APIsAttack surface monitoring to discover unmapped web endpoints
- L2Database & RepositoriesEliminate direct exposure of listener ports (MySQL 3306, PostgreSQL 5432)Enforce Principle of Least Privilege on service accountsEnable data-at-rest encryption and dynamic masking on DNI fieldsAudit telemetry for unauthorized dump utilities (mysqldump, pg_dump)
- L3Identity & Perimeter AccessEnforce phishing-resistant MFA on all administrative VPN and ZTNA gatewaysEnterprise-wide credential reset across provincial service accountsContinuous dark web monitoring for stolen infostealer credentials
Regulatory and Notification Exposure
Data breaches involving citizen registries trigger strict statutory scrutiny under national and international privacy frameworks. Argentine Personal Data Protection Law (Law 25,326) mandates rigorous technical and organizational measures to guarantee the confidentiality and integrity of citizen records. Public and private data controllers face regulatory enforcement from oversight authorities when data security standards fail.
Public institutions handling civic databases must evaluate several compliance imperatives:
Mandatory Security Audits: Regulators require verifiable proof that data-at-rest encryption, access logging, and privilege separation protocols were operational at the time of exfiltration.
Public Notification Obligations: While public disclosures must balance public order and security, regulatory precedents emphasize alerting impacted subjects when their official identity documents are circulating publicly, enabling them to monitor their personal credit reports and banking activities.
International Data Sharing Repercussions: For entities collaborating across regional trade groups or bilateral agreements, failing to protect civil identity repositories jeopardizes cross-border data transfer accreditations.
What to Check Now
Enterprise and public sector security leaders should initiate an immediate technical triage to verify whether similar vulnerabilities exist within their external perimeters. Evaluating your organization's posture requires inspecting access logs, hardening database connections, and validating edge application defenses.
Proactive validation should begin with regular assessments of outward-facing internet assets using comprehensive Attack Surface Management to discover forgotten subdomains and exposed database ports.
Database Audit and Log Inspection
Security teams should review database telemetry for indicators of bulk scraping or unauthorized schema dumping:
index=database (query="*SELECT*FROM*residentes*" OR query="*SELECT*FROM*ciudadanos*" OR query="*SELECT*FROM*padron*")
| stats count, sum(rows_returned) as total_rows by client_ip, user
| where total_rows > 5000
Examine database server event logs for the anomalous execution of utility binaries such as mysqldump, pg_dump, bcp, or mongodump originating from web application user accounts.
Immediate Remediation Checklist
Audit Public Application Endpoints: Perform automated and manual testing against all web APIs that accept citizen identification numbers to confirm that pagination parameters, rate limiting, and parameter binding are enforced.
Eliminate Direct Database Exposure: Ensure that database listener ports (such as MySQL 3306, PostgreSQL 5432, and MSSQL 1433) are strictly bound to internal interfaces and unreachable from the public internet.
Enforce Strict Least Privilege: Web application database service accounts must never possess administrative privileges or access to unrelated civil tables. Restrict bulk export and table modification permissions.
Deploy MFA on Administrative Gateways: Require phishing-resistant multi-factor authentication across all external VPN, RDP, and administrative management consoles to stop infostealer-led intrusions.
How to Defend Against Similar Threats
- Audit all public-facing application endpoints for SQL injection vulnerabilities and broken object-level authorization.
- Restrict database listeners to internal network segments and enforce hardware-backed MFA across remote administrative portals.
- Monitor dark web forums and underground channels for compromised organizational domains and credentials.
- Implement rate limiting and monitoring on database queries that touch citizen registry tables.
Threat Intel FAQ
What information was reportedly compromised in this incident?
Who is the threat actor behind this leak?
What immediate risks do exposed citizen records pose?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
September 20, 2026
Water Infrastructure Authority Database Leaked Online
A threat actor claims to have leaked more than 100,000 records from a public water management entity, exposing Peruvian national identity document numbers, citizen names, emails, and internal complaint registries.
An alleged data breach targeting Brazilian payment gateway and digital banking platform PagBank has surfaced on underground forums. A threat actor claims to possess a database containing information related to 10 billion transactions, highlighting the growing cybersecurity risks facing the fintech sector.
October 14, 2026
Fintech Payment Gateway Leaks 100,000 Billing Records
A threat actor claims to have published approximately 100,000 billing, payment, and customer records from a prominent Cambodian payment gateway on an underground forum, highlighting significant operational and fraud risks for integrated merchants and consumers.