Fintech Payment Gateway Leaks 100,000 Billing Records
A threat actor claims to have published approximately 100,000 billing, payment, and customer records from a prominent Cambodian payment gateway on an underground forum, highlighting significant operational and fraud risks for integrated merchants and consumers.
Key Takeaways
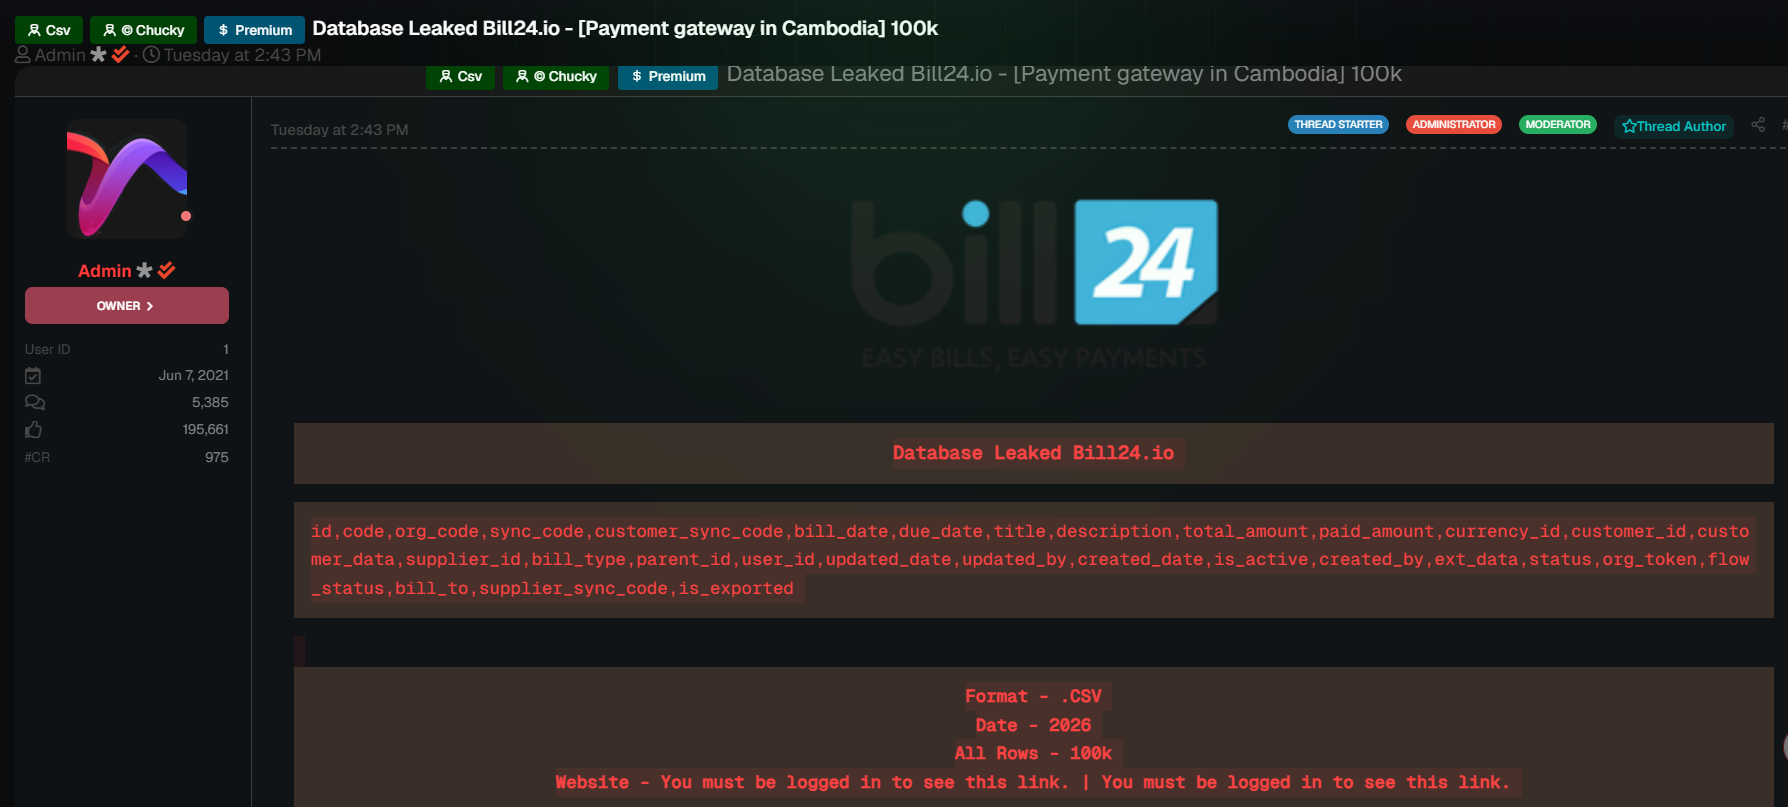
- Approximately 100,000 billing, payment, and customer records from payment gateway BILL 24 Co., Ltd. were allegedly leaked on Leakbase.
- The compromised data includes sensitive billing metadata, supplier profiles, invoice dates, and payment processing statuses.
- Exposed transaction telemetry creates substantial risks for invoice manipulation, business email compromise, and targeted consumer phishing.
- Downstream partners and financial institutions must audit integration secrets, rotate shared API keys, and enforce out-of-band verification on payment modifications.
An underground database dump containing approximately 100,000 structured billing and transaction records has surfaced on the cybercrime forum Leakbase, attributed to Cambodian payment integration provider BILL 24 Co., Ltd. The exfiltrated dataset, packaged in comma-separated values (CSV) format, encompasses sensitive commercial transaction histories, merchant ledger entries, customer contact identifiers, invoice dates, and internal system metadata. For financial institutions and merchants operating across Southeast Asia and international processing corridors, this incident underscores the severe secondary exposure created when centralized billing automation platforms suffer confidentiality breakdowns.
Scope of Alleged Exposure
What Was Exposed in the Transaction Dataset
The unauthorized listing claims to provide unfiltered access to back-office operational tables maintained by the payment gateway platform. While raw database dumps often contain incomplete remnants, the structure of this release points to direct table extraction or automated report harvesting from core billing environments.
According to the listing metadata and intelligence analysis, the compromised fields comprise several sensitive operational attributes:
Customer Personally Identifiable Information: Full names, billing contacts, and communication records linked directly to consumer payment attempts.
Merchant and Supplier Data: Enterprise supplier registries, merchant profile identifiers, and downstream vendor references.
Transaction Financial Metadata: Concrete transaction sums, currency entries, payment statuses (including successful, pending, and failed states), and specific invoice processing dates.
System Identifiers and Internal Account Metadata: Internal database primary keys, account linkage hashes, and billing reconciliation tokens used across the payment pipeline.
The presence of detailed transaction statuses paired with supplier records presents an acute commercial exposure. Unlike simple credential dumps containing unsorted usernames and passwords, structured billing records offer immediate utility for fraudulent exploitation, corporate impersonation, and invoice manipulation schemes.
Compromised Data Categories
- Customer PII & Contactshigh
- Merchant & Supplier Registrieshigh
- Transaction Sums & Statuseshigh
- Internal Reconciliation Keysmedium
How the Data Leak and Unauthorized Access Occurred
While the affected organization has not issued a technical post-mortem detailing the root cause of the intrusion, threat intelligence indicators and typical threat patterns targeting payment processing architectures point to several probable exfiltration vectors.
1. Application and API Authorization Flaws
Modern payment gateways rely heavily on RESTful APIs and microservice endpoints to communicate with banking entities, microfinance institutions, and utility providers. Vulnerabilities such as Broken Object Level Authorization (BOLA), insecure direct object references (IDOR), or unauthenticated export endpoints frequently allow external actors to systematically query and enumerate transaction sequences. When API gateways lack rigorous rate limiting and token scope validation, automated extractors can rapidly iterate through account identifiers and drain complete database schemas without triggering basic volumetric alerts.
2. Administrative Credential Theft via Infostealer Malware
Infostealer families like Lumma, RedLine, and Vidar continuously harvest administrative browser sessions, database management console credentials, and virtual private network (VPN) authentication tokens across corporate endpoints. If an internal engineer or operations specialist experienced a device compromise, stored session cookies for platforms such as phpMyAdmin, cloud database interfaces, or custom administrative portals could allow adversaries to execute bulk SELECT queries and dump tables directly to CSV format without deploying local malware onto production servers.
3. Cloud Storage Misconfiguration and Backup Exposure
Database administrators frequently run scheduled database dumps to create point-in-time recovery archives. When these snapshots or analytical reporting exports are placed into misconfigured cloud storage repositories, such as public Amazon S3 buckets or open file transfer servers, threat actors scanning public IPv4 ranges can discover and download them without requiring privilege escalation. If an organization does not employ proactive Attack Surface Management to inventory external assets, these exposed repositories can remain accessible for months.
Threat Technique Mapping
Downstream Risk and Secondary Exploitation Vectors
When financial transaction datasets enter underground circulation, the threats extend far beyond the initial target entity. The threat actor published the collection within a premium tier on Leakbase, meaning motivated cybercriminals and financial fraud syndicates now hold actionable data against thousands of commercial relationships.
Invoice Redirection and Business Email Compromise
With precise knowledge of legitimate invoice dates, outstanding amounts, and supplier identifiers, adversaries possess the exact telemetry required to execute convincing Business Email Compromise (BEC) attacks. Threat actors can register lookalike domains mimicking legitimate utility companies or suppliers, initiate contact with affected accounts payable teams, and request bank account routing modifications under the guise of reconciling pending invoice amounts.
Targeted Phishing and Credential Harvesting
Consumers whose phone numbers, email addresses, and active billing arrangements appear in the dataset face sophisticated spear-phishing campaigns. Fraudsters commonly craft SMS and email lures referencing real transaction balances or alleged failed payment notices, directing victims to credential-harvesting portals designed to siphon banking credentials and one-time passwords (OTPs).
Erosion of Third-Party Trust in Open Banking Ecosystems
Payment aggregators serve as critical bridges connecting microfinance institutions, enterprise merchants, and commercial banks. When an aggregator suffers a data breach, integrated banking partners often must suspend API access or enforce mandatory security recertification. This operational friction degrades consumer trust and can introduce severe liquidity and reconciliation challenges across integrated platforms.
Underground Listing Attribution
- Motivation
- Financial (Monetization via VIP/Premium subscription access)
- Targets
- Payment gatewaysFintech platformsAggregator databases
- TTPs
- CSV database exfiltrationUnderground brokering on Leakbase
Regulatory and Notification Exposure for Financial Processors
Financial technology operations handle regulated financial records that trigger stringent reporting mandates across multiple jurisdictions. Even when an incident originates within an emerging financial ecosystem, cross-border payments often tie organizations to international compliance frameworks.
Key compliance and legal considerations include:
Mandatory Breach Notification: Regulatory bodies supervising payment service providers generally require prompt disclosure of data security failures involving financial metadata. Failure to disclose breaches within mandated operational windows invites regulatory sanctions and operational license reviews.
Payment Card Industry Standards: Although this leak centers on billing ledger records rather than primary payment card account numbers (PAN), the infrastructure supporting payment processing falls under rigorous scrutiny. Compromised environments often require mandatory independent forensic investigations to confirm whether cardholder data environments (CDE) remained isolated.
Third-Party Vendor Due Diligence: Downstream enterprises that contracted the gateway for utility collection face legal responsibilities to notify their end-users if customer identifiable information was compromised through their digital supply chain.
Continuous surveillance of threat actor infrastructure is critical to measuring exposure after a breach occurs. Organizations seeking to identify whether corporate identifiers or executive accounts have surfaced across underground forums can leverage ongoing Dark Web Monitoring to intercept compromised assets before fraud execution begins.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Defender Verification Checklist
- Rotate shared merchant webhook secrets and API tokensAssume shared operational tokens and service account secrets were exposed
- Audit database audit logs for mass extraction eventsCheck for unpaginated SELECT * queries or INTO OUTFILE commands
- Audit cloud storage permissions and bucket policiesVerify S3 and object storage access boundaries for backup archives
- Enforce out-of-band verification for payment alterationsRequire voice or cryptographic confirmation prior to routing updates
What to Check Now: Immediate Defender Actions
Security teams managing digital payment pipelines, partner integrations, or utility billing architectures should initiate defensive verification immediately to protect their ecosystems from secondary exploitation.
1. Verify API Integration Scope and Credentials
Examine all third-party API keys and merchant webhooks associated with billing aggregators. If an upstream or downstream provider suffers a suspected compromise, assume that shared secret keys and administrative API tokens may have been exposed. Invalidate and rotate all webhook secrets, service account credentials, and mutual authentication certificates immediately.
2. Conduct Deep Database and Storage Access Audits
Review database engine audit logs across production and analytical clusters for anomalous extraction behaviors. Search specifically for the following telemetry signals:
Large-scale query execution commands such as
SELECT *targeting customer, invoice, and merchant relationship tables without pagination filters.Unusual invocations of administrative export procedures, including
INTO OUTFILEor mass CSV generation jobs executed during non-standard operational hours.Unauthenticated or single-factor connections originating from unfamiliar autonomous system numbers (ASNs) or hosting providers to database management interfaces.
3. Harden Partner Communication and Reconciliation Workflows
Alert internal finance and accounts receivable teams to exercise elevated verification protocols for all incoming payment instructions. Enforce out-of-band verification via cryptographically signed communications or confirmed voice verification before altering supplier remittance accounts, regardless of whether the request includes authentic invoice numbers and legitimate balance totals.
How to Defend Against Similar Threats
- Rotate shared API keys, webhook signing secrets, and service credentials linked to third-party billing aggregators.
- Implement out-of-band validation procedures for any supplier or vendor requests to modify payment routing details.
- Audit database access logs and API gateways for unauthorized high-volume export commands and abnormal read volumes.
- Monitor dark web marketplaces and forum repositories for leaked corporate domain credentials and exposed supplier records.
Threat Intel FAQ
What specific data was reportedly compromised in the payment gateway breach?
How can threat actors exploit exposed billing and invoice records?
What immediate steps should organizations integrated with payment aggregators take?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
An alleged data breach targeting Brazilian payment gateway and digital banking platform PagBank has surfaced on underground forums. A threat actor claims to possess a database containing information related to 10 billion transactions, highlighting the growing cybersecurity risks facing the fintech sector.
October 16, 2026
Returnero Leaks 200,000 Government Records
A dark web forum breach exposing 200,000 citizen records has highlighted severe identity theft and social engineering risks across public administration databases. FemtoSec provides deep technical analysis of the exfiltration vectors, MITRE ATT&CK mapping, and actionable containment measures for security teams.
September 20, 2026
Water Infrastructure Authority Database Leaked Online
A threat actor claims to have leaked more than 100,000 records from a public water management entity, exposing Peruvian national identity document numbers, citizen names, emails, and internal complaint registries.