Dark Project Ransomware Hits US Machinery Sector
Dark Project ransomware operators have listed a US industrial machinery distributor on their dark web portal, threatening to leak 115 GB of proprietary project drawings, customer databases, and financial files following an aggressive extortion countdown.
Key Takeaways
- Dark Project extortion actors listed US manufacturer Pump Engineering Company on their dark web portal.
- The stolen dataset reportedly contains 115 GB of files, including customer databases, project drawings, and financial documents.
- A 9 to 10 day countdown was established by the attackers before threatened public release of the 120,000 exfiltrated files.
- Manufacturing organizations must enforce multi-factor authentication, segment engineering shares, and monitor for anomalous data egress.
Proprietary industrial schematics, confidential financial sheets, and comprehensive customer databases face public exposure when extortion operators breach critical engineering infrastructure. Industrial manufacturing firms remain primary targets for double-extortion syndicates seeking leverage over proprietary designs and trade secrets. The compromise of 115 GB of sensitive engineering records demonstrates how extortion groups exploit unprotected data repositories to maximize payment demands.
Pump Engineering Incident Scope
What Happened in the Attack
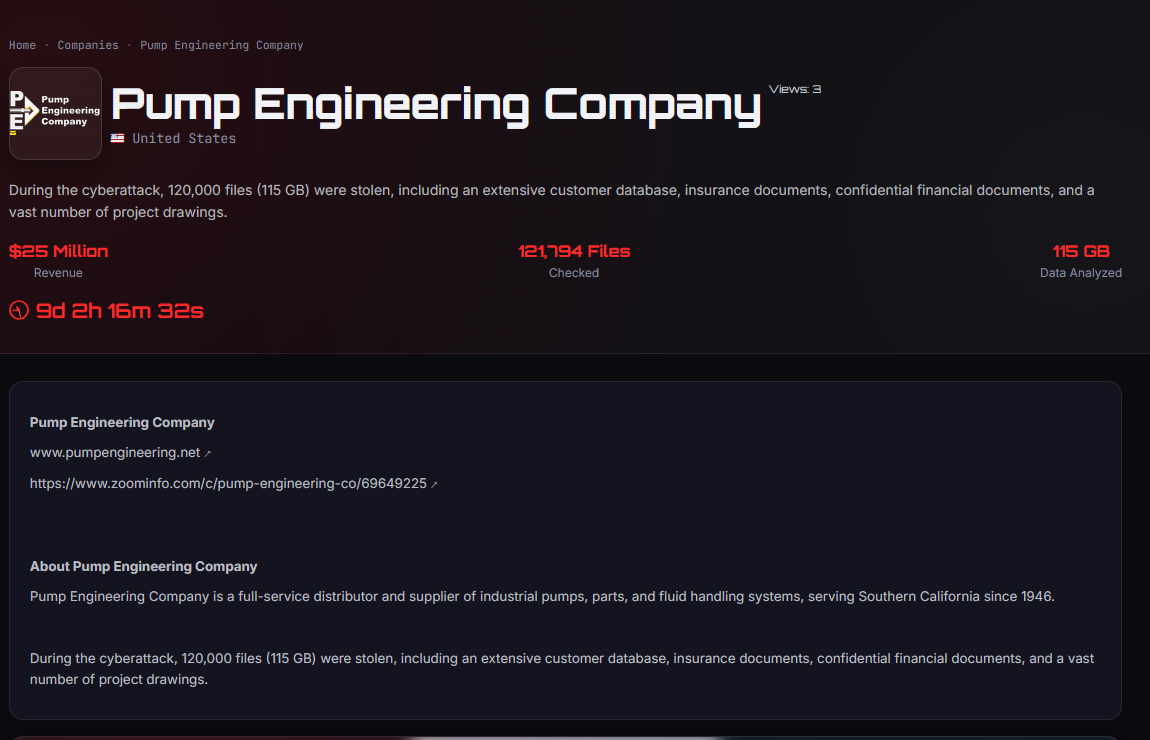
The extortion syndicate operating under the moniker Dark Project published a listing targeting Pump Engineering Company (pumpengineering.net), a United States distributor of industrial fluid handling and pump systems. The threat actors claim to have compromised and exfiltrated 115 GB of corporate data, representing approximately 120,000 distinct files.
According to the listing posted on the syndicate's Tor-based data leak site, the stolen archive comprises high-value corporate assets:
Proprietary Project Drawings: Technical schematics, engineering plans, and CAD files representing industrial equipment configurations.
Customer Database: Extensive operational and contact records detailing corporate clients, purchasing histories, and commercial contracts.
Confidential Financial Records: Internal balance sheets, accounting ledgers, and transaction documentation.
Insurance and Corporate Documents: Policy agreements, legal filings, and administrative governance records.
The threat actor established an extortion deadline of 9 to 10 days, threatening full public release of all 120,000 files if negotiation terms are not initiated. To gauge organizational exposure before leaks materialize, security teams can conduct a quick check.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Dark Project Attack Chain
- 1Initial Access
Opportunistic intrusion via exposed RDP/VPN or stolen credentials
- 2Internal Discovery
Staging CAD schematics (.dwg, .step) and accounting databases
- 3Data Exfiltration
Archiving and transfer of 115 GB to adversary infrastructure
- 4Extortion & Leak Listing
Tor leak portal posting with a 9-10 day public release countdown
How the Ransomware and Extortion Cycle Operates
Dark Project executes a structured double-extortion model designed to maintain financial leverage even if victim systems maintain resilient offline backups. The attack lifecycle unfolds across distinct stages:
1. Initial Access and Perimeter Infiltration
Extortion actors typically gain footholds in manufacturing environments through opportunistic access vectors. Common intrusion pathways include exposed remote access portals such as Remote Desktop Protocol (RDP) or Virtual Private Network (VPN) appliances lacking multi-factor authentication (MFA). Stolen corporate credentials, frequently harvested by commercial infostealer malware, provide attackers with direct access through valid administrative or employee sessions (MITRE ATT&CK T1078, T1133).
Organizations can identify perimeter vulnerabilities and exposed management interfaces before adversaries exploit them by utilizing continuous Attack Surface Management.
2. Internal Discovery and Data Staging
Once inside the internal boundary, operators execute discovery scripts to identify centralized repositories, network-attached storage (NAS) devices, and Active Directory file shares (MITRE ATT&CK T1083). Attackers specifically target file extensions linked to proprietary designs (.dwg, .dxf, .step, .pdf) and enterprise finance (.xlsx, .qbb, .accdb).
3. Data Exfiltration
Prior to deploying any destructive payload or announcing their presence, the threat actors stage gathered data into compressed, encrypted archives. The data is exfiltrated to threat actor-controlled command and control servers or cloud storage providers using encrypted outbound protocols or command-line utilities (MITRE ATT&CK T1567).
4. Extortion and Leak Site Publication
Upon completing the exfiltration of the target directory trees, Dark Project publishes victim proof-of-compromise packages on their hidden service portal, initiating communications over secure channels such as Tox and OnionMail.
Dark Project MITRE ATT&CK Mapping
Who Is Behind the Dark Project Group
Dark Project is an emerging cyber extortion group that surfaced on underground monitoring channels in August 2026. The syndicate specializes in extortion-driven intrusions against commercial enterprises across North America, targeting sectors including machinery manufacturing, commercial services, and healthcare.
Unlike pure encryption operations, Dark Project places heavy emphasis on intellectual property theft, utilizing stolen trade secrets and customer records as primary leverage points. The group maintains direct communication channels through specific operational handles:
Tor Leak Site:
http://darkprn3d3udnhpuxknsrhft3376lrz5tenhgkrxge5hxqe46pkbrwid.onionOperational Email:
[email protected]Tox Chat Identifier:
243AAD0D1875CA4D48034E799785F2C9EA225E4466C87FA9B9297F7BEADC694478C7DE0A7639
The group's operational pattern suggests an opportunistic targeting strategy, focusing on organizations with valuable intellectual property but potentially less segmented internal network architectures.
Adversary Profile: Dark Project
- Motivation
- Financial (Double Extortion)
- Targets
- Machinery & ManufacturingHealthcareCommercial ServicesNorth America
- TTPs
- Opportunistic credential & perimeter exploitationTargeted theft of CAD & proprietary blueprintsTor-hosted proof-of-compromise leak listingsDirect extortion via Tox and OnionMail
Enterprise Impact and Extortion Pressure
The theft of 120,000 corporate files introduces multifaceted operational, legal, and reputational challenges for mid-market and enterprise industrial suppliers.
Loss of Proprietary Intellectual Property
For engineering and equipment manufacturers, CAD drawings and project schematics represent foundational competitive assets. The public exposure or illicit sale of these blueprints allows competitor duplication, compromises proprietary fabrication methodologies, and voids customer confidentiality agreements regarding bespoke system engineering.
Supply Chain and Customer Exposure
Customer databases containing transaction histories, equipment delivery addresses, and purchasing points expose downstream enterprise clients to targeted phishing, business email compromise (BEC), and supply chain scrutiny. Commercial partners may audit supplier cybersecurity compliance following disclosure.
Regulatory and Legal Liabilities
The exfiltration of employee insurance records and corporate financial documentation triggers mandatory breach notification protocols under state and federal data protection frameworks, exposing organizations to regulatory investigations and litigation.
Dark Project Extortion Infrastructure
- urlhttp://darkprn3d3udnhpuxknsrhft3376lrz5tenhgkrxge5hxqe46pkbrwid.onionDark Project Tor Data Leak Site (DLS)urlhttp://darkprn3d3udnhpuxknsrhft3376lrz5tenhgkrxge5hxqe46pkbrwid.onionDark Project Tor Data Leak Site (DLS)
- emailActor contact email
Detection and Containment Strategies
Defending against opportunistic extortion operators requires systematic logging, strict boundary controls, and continuous offensive security validation.
Detection Logic and Threat Hunting Queries
Security operations center (SOC) teams should configure detection rules to identify unauthorized data collection and exfiltration activities:
Tor and Anonymization Traffic: Alert on any perimeter outbound connections to Tor entry guards or unusual DNS queries resolving .onion proxy domains.
Abnormal Data Egress: Monitor egress bandwidth thresholds for sudden spikes in outbound HTTPS, SFTP, or cloud storage connections originating from file servers or CAD repositories.
Unusual Remote Authentication: Flag multiple sequential VPN authentication failures followed by successful logins from unfamiliar geographical regions or anomalous IP addresses.
Archive Staging Activity: Detect unusual executions of archiving tools (such as
7z.exe,rar.exe, ortar.exe) within non-standard directories (e.g.,C:\Users\Public\,C:\ProgramData\).
Immediate Containment Playbook
If an organization detects unauthorized access or anomalous activity indicative of an extortion intrusion, the following steps must be initiated immediately:
Isolate Impacted Systems: Disconnect affected endpoints, servers, and storage clusters from the corporate network at the switch or virtual interface level. Avoid powering down machines to preserve volatile memory artifacts.
Revoke Remote Sessions: Terminate all active VPN, RDP, and remote management tool sessions across the enterprise gateway.
Enforce Global Credential Rotation: Execute an immediate password reset for all Active Directory user accounts, domain administrators, service accounts, and remote access tokens.
Audit Perimeter Access: Enforce mandatory hardware-backed or application-based Multi-Factor Authentication (MFA) across all external-facing administrative portals and cloud management consoles.
Preserve Forensic Telemetry: Secure firewall logs, NetFlow records, authentication histories, and endpoint event logs to enable comprehensive intrusion reconstruction.
Proactive security validation through regular simulated attacks identifies critical exposure vectors before malicious actors discover them. Organizations can evaluate internal resilience by scheduling comprehensive Penetration Testing to harden network boundaries, segment sensitive repositories, and neutralize attack chains.
How to Defend Against Similar Threats
- Enforce multi-factor authentication across all external VPN, RDP, and remote administration interfaces.
- Implement egress filtering and bandwidth alerting to detect massive archival file transfers from internal repositories.
- Segment network zones hosting proprietary engineering files, CAD drawings, and financial databases from general user networks.
- Perform periodic dark web exposure audits to detect compromised corporate credentials from botnets.
Threat Intel FAQ
What data did Dark Project claim to exfiltrate?
How do extortion groups like Dark Project gain initial access?
What should organizations do if proprietary drawings are threatened with public leak?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 23, 2026
Kazu Ransomware Targets Insurance Sector in 366 GB Breach
Kazu ransomware operators have listed South African insurer Rand Mutual Assurance on their dark web leak portal, claiming 366 GB of exfiltrated corporate records. This intelligence brief examines Kazu's attack tradecraft, LockBit lineage, operational impact, and concrete detection rules.
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.