Kazu Ransomware Targets Insurance Sector in 366 GB Breach
Kazu ransomware operators have listed South African insurer Rand Mutual Assurance on their dark web leak portal, claiming 366 GB of exfiltrated corporate records. This intelligence brief examines Kazu's attack tradecraft, LockBit lineage, operational impact, and concrete detection rules.
Key Takeaways
- Kazu ransomware listed Rand Mutual Assurance, claiming 366 GB of proprietary data under a 12 to 13 day countdown timer.
- Kazu utilizes a double-extortion operational model leveraging LockBit-derived payloads for Windows and Linux/ESXi environments.
- Initial access typically stems from broker-acquired credentials, infostealer logs, or internet-facing appliance vulnerabilities.
- Immediate containment requires privileged account rotation, hypervisor segmentation, and air-gapped immutable backup validation.
Massive operational disruption and severe regulatory liability loom over organizations when enterprise repositories fall to extortion operators. In South Africa, mutual insurance administrator Rand Mutual Assurance (RMA) became the latest high-profile victim after the Kazu ransomware group published an extortion listing claiming the theft of 366 GB of proprietary data. The threat actors established a countdown ultimatum demanding compliance within 12 to 13 days under the threat of public distribution across dark web portals and underground channels.
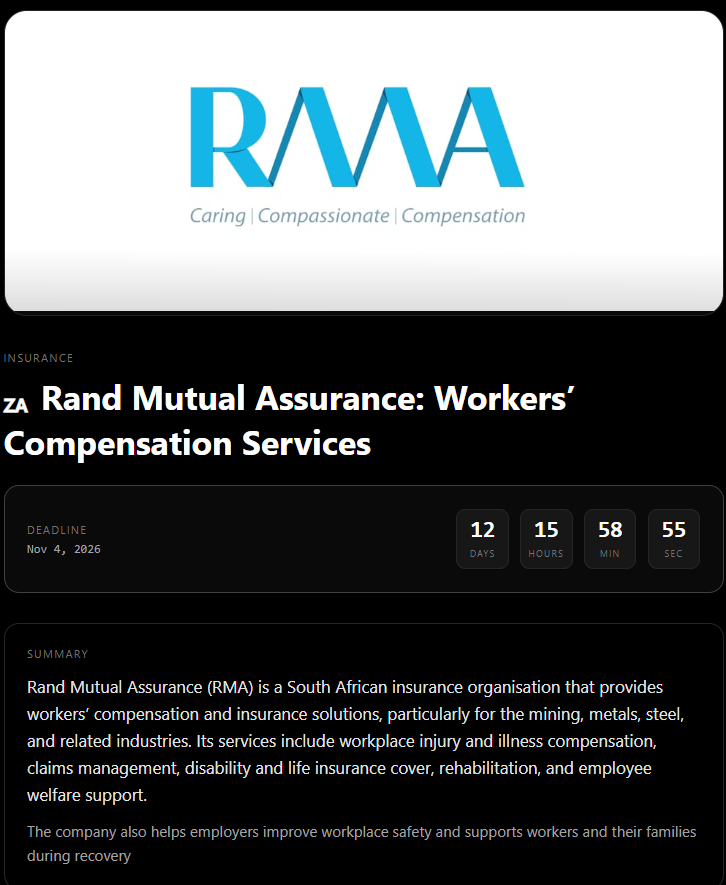
Rand Mutual Assurance Incident Parameters
What Happened in the Rand Mutual Assurance Incident
Rand Mutual Assurance, an organization administering medical claims, compensation, and benefits for occupational injuries across critical industrial sectors, was listed on the official Tor-based data leak site of the Kazu ransomware group. According to the syndicate's disclosure, the intrusion resulted in the compromise and extraction of 366 GB of sensitive internal files. The threat actors subsequently initiated a timed countdown, asserting that all exfiltrated archives would be released publicly if negotiations failed.
The targeting of an insurance administrator exposes substantial quantities of confidential policyholder records, identity documents, and claims adjudications. The double-extortion framework utilized by Kazu exerts immense leverage by combining operational downtime with severe compliance consequences under data protection frameworks like South Africa's Protection of Personal Information Act (POPIA). Organizations operating in comparable sectors must assess their exposure using proactive penetration testing to uncover the access pathways adversaries exploit before data theft occurs.
Rand Mutual Assurance Blast Radius
- Occupational Injury Claimshigh
- Confidential Policyholder Recordshigh
- Identity & Compensation Datahigh
- POPIA Regulatory Liabilityhigh
How the Ransomware Operates Across Enterprise Networks
Kazu functions as a double-extortion ransomware threat group that surfaced in late 2025 and escalated operations through 2026. Security researchers have identified Kazu's cryptographic payload as an evolution derived from leaked LockBit codebases, specifically inheriting architectural similarities from LockBit 3.0 builders. The malware family features both Windows binaries and specialized Linux builds designed to terminate and encrypt VMware ESXi virtual machine volumes (.vmdk files).
Phase 1: Initial Access and Perimeter Exploitation
Kazu operators rarely rely on novel zero-day exploits, instead sourcing network entry via initial access brokers (IABs) and internet-facing application weaknesses. The group frequently capitalizes on compromised administrative credentials obtained from infostealer malware logs, credential stuffing campaigns against enterprise portals, and opportunistic exploitation of unpatched perimeter hardware like remote desktop interfaces, VPN appliances, and external firewalls (MITRE ATT&CK T1078, T1190). Continuous exposure verification through attack surface management is vital to discovering these exposed edge systems before threat actors do.
Phase 2: Execution, Staging, and Evasion
Once inside a victim's network, the adversaries execute malicious PowerShell and command-line scripts to assess environment parameters and disable standard security defenses (T1059.001, T1059.003). In multiple campaigns, Kazu operators drop secondary utility payloads, such as SmokeLoader, to stage execution routines and facilitate tool delivery without triggering basic heuristic alerts (T1105). To prevent recovery and evasion inspection, the operators execute defensive impairment routines, terminating endpoint detection agents and removing local volume shadow copies through automated shell instructions (T1562.001, T1490).
Phase 3: Lateral Movement, Data Exfiltration, and Encryption
Adversaries maneuver laterally across Active Directory subnets using administrative remote management protocols including Remote Desktop Protocol (RDP), Server Message Block (SMB), and Windows Management Instrumentation (WMI) (T1021.001, T1021.002). The operators target domain controllers, core file shares, and hypervisors. Before initiating the multithreaded encryption phase (T1486), the operators stage and compress proprietary directories into centralized staging folders, subsequently transferring high-volume data archives outbound over command-and-control channels (T1048, T1041). Once extraction is confirmed, the ransomware encrypts targeted systems, appends victim-specific file extensions, and drops extortion notices throughout altered directories.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Kazu Intrusion and Extortion Lifecycle
- 1Initial Access
Valid accounts (T1078) & edge service exploitation (T1190)
- 2Execution & Staging
PowerShell (T1059.001) & SmokeLoader staging (T1105)
- 3Defense Impairment
EDR termination & shadow copy purge (T1562.001, T1490)
- 4Lateral Traversal
RDP, SMB, and WMI across domain subnets (T1021)
- 5Exfiltration & Encryption
366 GB transfer (T1048) & LockBit-based multithreaded encryption (T1486)
Who Is Behind It: Profiling the Kazu Threat Group
The Kazu ransomware operation emerged during the final quarter of 2025, operating an aggressive affiliate-style extortion model. The syndicate maintains an extensive technical presence across the Tor network, managing multiple mirrored leak sites, Debian-hosted proxy frontends, and backup communication conduits across privacy-focused messaging services including Session, Telegram, and Proton Mail.
Rather than developing an entirely bespoke cryptographic engine, Kazu adopted the tactical playbook seen in multiple post-LockBit offshoots. By retooling proven encryptor architectures, the operators achieve rapid multithreaded encryption performance and cross-platform flexibility across Windows and ESXi infrastructure. Their target portfolio spans multiple geographic regions, notably focusing on mid-market and enterprise entities across healthcare, government, education, and financial services in Latin America, Asia, the Middle East, and Africa.
Adversary Profile: Kazu Ransomware Group
- Motivation
- Financial (Double Extortion)
- Targets
- InsuranceHealthcareGovernmentEducationFinancial Services
- TTPs
- LockBit 3.0 builder derivationESXi VMDK encryptionSmokeLoader initial dropsTor DLS and Telegram/Session negotiation
Enterprise Impact and Extortion Pressure
Double-extortion attacks against insurance and claims organizations introduce compounding business risks that extend far beyond initial host lockout. The potential release of 366 GB of administrative records presents three immediate layers of enterprise harm:
Severe Regulatory Exposure: Under data privacy mandates such as POPIA, the unauthorized exposure of personally identifiable information (PII), banking details, and medical records mandates strict disclosure deadlines and carries substantial administrative penalties.
Secondary Fraud and Supply Chain Risk: The compromise of claims data provides cybercriminals with granular identity assets, enabling targeted spear-phishing, business email compromise (BEC), and medical identity theft against affiliated companies and claimants.
Protracted Operational Downtime: If core infrastructure or virtualization environments are locked during encryption, enterprise claims adjudication and payout pipelines halt completely, causing acute brand damage and operational gridlock.
Detection and Containment Strategies
Defenders must deploy immediate detection telemetry and proactive containment controls to intercept Kazu intrusions prior to bulk exfiltration and encryption execution. Security operations teams should implement the following validation rules and immediate containment steps.
Endpoint and SIEM Detection Rules
Monitor Windows Event Logs and endpoint telemetry for anomalous process invocations aimed at eliminating recovery options. Security incident platforms should flag command line arguments attempting shadow copy deletion and boot configuration tampering:
index=* (EventCode=4688 OR process_name="cmd.exe" OR process_name="powershell.exe")
| search CommandLine="*vssadmin*delete*shadows*"
     OR CommandLine="*wbadmin*delete*catalog*"
     OR CommandLine="*bcdedit*/set*bootstatuspolicy*ignoreallfailures*"
     OR CommandLine="*bcdedit*/set*recoveryenabled*no*"
Technical Indicators of Compromise
Security operations centers should immediately cross-reference environment logs against identified Kazu payload hashes and operational network infrastructure:
SHA-256 (Ransomware Payload):
7ea5afbc166c4e23498aa9747be81ceaf8dad90b8daa07a6e4644dc7c2277b82MD5 (Ransomware Payload):
95daa771a28eaed76eb01e1e8f403f7cMD5 (SmokeLoader Stager):
e818a9afd55693d556a47002a7b7ef31Hosting Infrastructure IPv4:
23.137.255.139Known Onion Leak Mirrors:
6czlbd2jfiy6765fbnbnzuwuqocg57ebvp3tbm35kib425k4qnmiiiqd.onion,kazusemtykpxnnosg3gp56spcdkg7tro6ozei7ikamdgnwpwpbwagbyd.onion
Immediate Containment Playbook
Privileged Account Revocation: Force an enterprise-wide reset of Active Directory domain administrative credentials, service accounts, and enterprise administrator accounts. Invalidate all active session tokens across single sign-on (SSO) and VPN gateways.
Hypervisor and Storage Segmentation: Isolate management interfaces for virtualization clusters (VMware ESXi, vCenter) onto non-routable administrative VLANs with strict jump-host requirements to protect virtual disk volumes.
Egress Anomaly Inspection: Configure network perimeter alerts for large outbound data transfers (>50 GB) toward external storage providers, mega services, or anomalous cloud IP ranges.
Immutable Backup Isolation: Verify that enterprise recovery repositories are completely air-gapped, write-protected, and isolated from Active Directory trust domains to guarantee restoration without paying extortion ransoms.
How to Defend Against Similar Threats
- Audit and enforce phishing-resistant MFA across all remote access, VPN, and cloud administrator interfaces.
- Implement process-level monitoring for shadow copy deletion commands and unusual mass file modifications.
- Isolate VMware ESXi and virtualization management networks from general corporate IT subnets.
- Run dark web and exposure evaluations to identify compromised credentials circulating on underground broker channels.
Threat Intel FAQ
What is Kazu ransomware and what are its origins?
What data did Kazu claim to steal from Rand Mutual Assurance?
How do Kazu operators typically gain initial access to enterprise networks?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
The Delhi Heart and Lung Institute has fallen victim to a major breach by the Krybit ransomware syndicate. The threat actors claim to have exfiltrated 22 GB of sensitive hospital, patient, employee, and corporate data, threatening public release within a short four-day window.
July 31, 2026
Everest Ransomware Group Extorts Rx Networks Inc
The Everest ransomware group has compromised Canadian telecommunications provider Rx Networks Inc, claiming to have exfiltrated 321 GB of corporate data. Discover the deep technical mechanics of Everest's attack chain, defense evasion, hostile Wake-on-LAN sweeps, and enterprise detection rules.
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.