Black Nevas Ransomware Targets Omani Enterprise
A confirmed ransomware attack by the Black Nevas group has targeted Oman-based conglomerate OTE Group. The threat actors claim to have exfiltrated sensitive organizational data, signaling a rising risk to critical enterprise supply chains and automotive distributors across the GCC region.
Key Takeaways
- Black Nevas ransomware has claimed an attack against OTE Group, a prominent distributor in Oman.
- The incident highlights the growing interest of emerging ransomware groups in Middle Eastern enterprises, particularly within the automotive and logistics sectors.
- Implementing continuous monitoring and proactive offensive validation remains critical to disrupting initial access vectors before encryption occurs.
Disrupting supply chains and stalling distribution networks represent the primary operational impacts when a major regional conglomerate falls victim to ransomware. The compromise of OTE Group, a prominent automotive and consumer electronics distributor in Oman, by the Black Nevas ransomware group illustrates how threat actors leverage operational downtime to enforce extortion demands. When core logistical systems are compromised, the immediate fallout involves halted inventory tracking, delayed customer deliveries, and potential exposure of corporate databases. This incident highlights the vulnerability of regional supply chain hubs to modern double-extortion tactics, where stolen data is weaponized alongside system encryption to maximize leverage.
What Happened
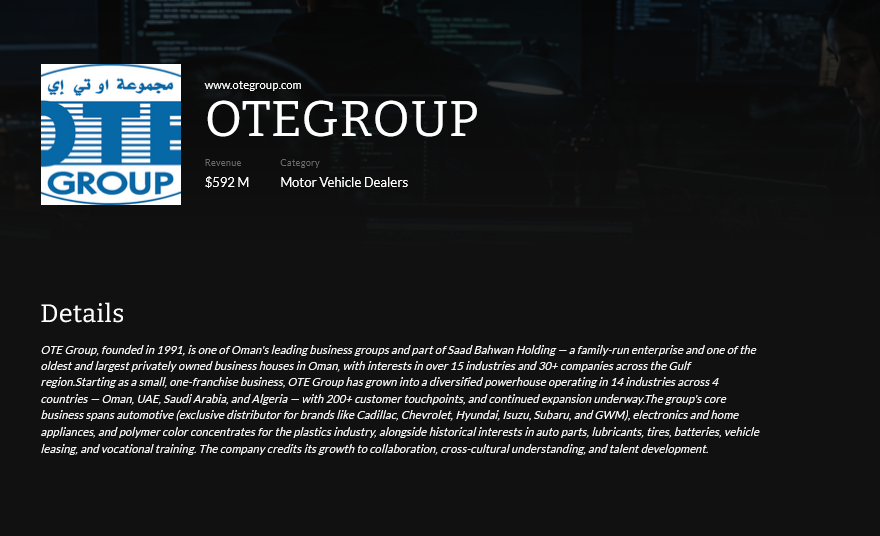
The security incident involving OTE Group came to light following claims by the Black Nevas ransomware group. According to indicators published on the threat actor's Tor-based leak site, the group successfully breached the corporate network and exfiltrated sensitive organizational data. OTE Group, operating under the domain otegroup.com, is a major business conglomerate in Oman with extensive operations in automotive distribution, auto leasing, consumer electronics, and vocational training.
While the exact initial access vector has not been publicly disclosed, ransomware groups operating in the GCC region frequently exploit unpatched edge devices or compromise credentials harvested through phishing campaigns. The threat actors assert that they hold a substantial volume of the organization's internal data, which they threaten to release if their extortion demands are not met. For large-scale distributors, such an attack does not merely affect internal operations; it ripples outward to affect international manufacturers, local dealerships, and thousands of retail customers who rely on their supply chains daily.
To identify where your organization might be vulnerable to similar initial access vectors, conducting comprehensive Attack Surface Management can map your external footprint and uncover exposed services before malicious actors exploit them. Proactive discovery remains the most reliable defense against the automated scanners utilized by ransomware affiliates.
Threat Actor Profile
- Motivation
- Financial (Double-Extortion)
- Targets
- Middle Eastern EnterprisesOmani ConglomeratesAutomotive and Consumer Electronics Sectors
- TTPs
- Ransomware-as-a-Service (RaaS) modelDouble-extortion tacticsExfiltration prior to encryptionBackup deletion
How the Ransomware Operates
Although Black Nevas is a relatively new or less-documented name in the threat landscape, its behavior aligns closely with modern Ransomware-as-a-Service (RaaS) models. Ransomware operations typically follow a structured attack chain designed to establish persistent access, escalate privileges, and bypass local security controls before initiating the final encryption phase.
The typical attack sequence of such ransomware includes the following phases:
Initial Access: Attackers gain entry using compromised remote desktop protocol (RDP) credentials, exploiting vulnerabilities in virtual private networks (VPNs), or utilizing sophisticated phishing lures directed at high-privilege employees.
Credential Harvesting and Lateral Movement: Once inside the network, the operators deploy tools like Mimikatz or access system memory to extract credentials. They then use native administrative utilities (often referred to as living-off-the-land techniques) such as PowerShell and Windows Management Instrumentation (WMI) to move laterally across the network.
Data Exfiltration: Prior to executing the encryption payload, the actors identify high-value targets including financial files, employee databases, proprietary designs, and strategic plans. They stage this data and exfiltrate it to attacker-controlled command and control (C2) servers using protocols like SFTP or cloud storage tools.
Inhibiting System Recovery: To prevent easy restoration, the malware targets volume shadow copies, system backups, and recovery partitions. Commands such as
vssadmin.exe delete shadows /all /quietare executed globally across all compromised endpoints.Encryption and Ransom Note Deployment: The ransomware deploys a custom cryptographic routine (often utilizing a combination of AES-256 and RSA-2048) to lock files. It appends a distinct extension to encrypted files and drops a ransom note instructing the victim to contact the operators via a Tor portal.
Black Nevas Attack Sequence
- 1Initial Access
RDP, VPN, or Phishing
- 2Credential Harvesting
Mimikatz & local tools
- 3Data Exfiltration
SFTP or cloud upload
- 4Inhibit Recovery
Delete shadow copies
- 5Encryption
AES-256 + RSA-2048
Technological Delivery Mechanisms
Modern RaaS operators leverage highly modular code bases to build their payloads. The binary often utilizes obfuscation techniques to bypass static signature analysis. Security teams should analyze system logs for the execution of unusual binaries from temp directories, unexpected modification of registry keys associated with boot configurations, and attempts to stop security-critical services. Ransomware groups are also known to use dual-use tools, such as remote monitoring and management (RMM) software, to maintain persistence even after initial backdoors are remediated.
Observed Cyber Kill Chain Coverage
- Reconnaissance
- Weaponization
- DeliveryPhishing, RDP, or VPN exploitation
- ExploitationBypassing local security controls
- InstallationDeploying modular ransomware binary
- Command & ControlExfiltration to actor-controlled servers
- Actions on ObjectivesAES-256/RSA-2048 encryption & extortion
- 01Reconnaissance
- 02Weaponization
- 03DeliveryPhishing, RDP, or VPN exploitation
- 04ExploitationBypassing local security controls
- 05InstallationDeploying modular ransomware binary
- 06Command & ControlExfiltration to actor-controlled servers
- 07Actions on ObjectivesAES-256/RSA-2048 encryption & extortion
Who Is Behind It
The attribution of this attack points directly to the Black Nevas ransomware operators, a threat actor group emerging on the dark web. Like many contemporary cybercriminal collectives, this group operates on a double-extortion model, aiming to extract payments by threatening both permanent data loss and public exposure of proprietary corporate information.
Emerging threat groups often lease their builder software to independent affiliates, meaning that the technical sophistication of individual campaigns can vary. These affiliates are highly opportunistic, scanning global IP ranges for low-hanging fruit such as unpatched vulnerabilities or weak authentication portals. The targeting of an Omani automotive conglomerate suggests that Middle Eastern enterprises are increasingly viewed as lucrative targets due to their critical role in regional commerce and their high-value asset bases.
To defend against these multi-stage tactics, enterprises must evaluate their readiness against real-world adversaries. Utilizing professional Red Teaming simulations allows organizations to test their detection, response, and containment capabilities against simulated attack paths that mimic the exact techniques deployed by groups like Black Nevas.
Attribution and Regional Targeting Context
The rise of Black Nevas highlights a broader trend of decentralized cybercrime networks targeting specific geopolitical regions. In the Middle East, and particularly within the GCC, rapid digitalization combined with high economic value makes local enterprises prime targets. While some campaigns are highly targeted and executed by persistent threat actors, others are opportunistic, initiated by scanning tools that locate exposed systems on the internet. Because the barrier to entry for launching a ransomware campaign is lower than ever due to RaaS kits, organizations must treat every exposed port as a critical vulnerability.
Enterprise Impact and Extortion Pressure
The operational impact of a successful ransomware deployment against a major distributor like OTE Group is multi-dimensional, extending far beyond the immediate IT department. In the automotive sector, supply chain continuity is vital. A disruption to logistics databases can halt parts distribution, prevent vehicle servicing, and freeze sales pipelines across multiple regional showrooms.
Furthermore, the extortion pressure applied during these attacks is designed to create maximum urgency. The double-extortion tactic places organizations in a difficult position: even if they possess robust, offline backups capable of restoring operations, the threat of proprietary data being leaked online introduces severe compliance, reputational, and legal risks. In the GCC region, strict data protection laws mean that a public leak of customer or employee data can result in substantial regulatory penalties and a loss of trust among long-term business partners.
When organizations face potential data exposure, understanding what information has already leaked into the public domain is crucial. Free domain exposure scan: Use FemtoSec's Dark Web Scanner to check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Proactive Defense and Detection Layers
- L1PerimeterSecure external RDP & VPN interfacesDeploy Attack Surface Management to map footprint
- L2NetworkMonitor for unexpected SFTP or cloud transfersLog PowerShell and WMI administrative commands
- L3EndpointDeploy EDR to block rapid file modificationMonitor for unusual binaries running from temp folders
- L4Backup & RecoveryKeep isolated, offline backupsVerify backup integrity regularly
Detection and Containment
Proactive Detection Strategies
Defenders should focus on identifying the behaviors that precede encryption, as these provide the highest-fidelity alerts:
Monitor PowerShell and WMI Abuse: Implement logging for command-line arguments that indicate administrative abuse, such as encoded PowerShell commands, attempts to disable security agents, or remote service creation.
Track Unusual Data Movement: Establish baseline thresholds for outbound data flows. Large volumes of data being sent to unrecognized external cloud services or IP addresses should trigger immediate containment protocols.
Endpoint Detection and Response (EDR): Configure EDR policies to block known ransomware behaviors, including the rapid modification of file extensions and the deletion of backup shadow copies.
Containment and Response Protocols
If an active intrusion or suspicious credential usage is detected, security administrators must execute the following containment actions immediately:
Isolate Affected Hosts: Segment compromised workstations and servers from the wider corporate network to prevent lateral movement. Do not power down machines immediately if memory forensics is required, but sever their network connections.
Revoke Compromised Credentials: Perform a global reset of administrative passwords and invalidate active session tokens across the entire domain, especially for external-facing systems like VPNs and cloud portals.
Verify Backup Integrity: Inspect and isolate backup storage solutions to ensure they have not been accessed or altered by the threat actors before initiating any system recovery processes.
Incident Containment & Response Checklist
- Isolate Affected HostsSegment compromised workstations and servers; do not shut down immediately if memory forensics is needed
- Revoke Compromised CredentialsGlobal administrative password reset and session token invalidation, especially for external portals
- Verify Backup IntegrityInspect and isolate backup storage systems prior to initiating restore processes
How to Defend Against Similar Threats
- Conduct a thorough assessment of all public-facing assets to identify potential entry points for threat actors.
- Perform regular penetration testing and vulnerability management to secure active directories and endpoints.
- Establish offline, immutable backups and test restoration protocols to ensure operational resilience during a cyber incident.
Threat Intel FAQ
What is the Black Nevas ransomware group?
How can GCC enterprises protect themselves against Black Nevas attacks?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 23, 2026
Kazu Ransomware Targets Insurance Sector in 366 GB Breach
Kazu ransomware operators have listed South African insurer Rand Mutual Assurance on their dark web leak portal, claiming 366 GB of exfiltrated corporate records. This intelligence brief examines Kazu's attack tradecraft, LockBit lineage, operational impact, and concrete detection rules.
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.