Vexy Ransomware Targets Retailer in 24GB Data Leak
The Vexy ransomware group has published an extortion listing targeting Argentinian retailer Librería Santa Fe, claiming 24.2 GB of exfiltrated data with a 20-day publication ultimatum. Explore technical analysis, attack chains, and defensive containment strategies.
Key Takeaways
- The Vexy ransomware group added Argentinian bookstore chain Librería Santa Fe to its Tor leak site on September 7, 2026.
- The threat group claims to have exfiltrated 24.2 GB of corporate data, setting a 19 to 20-day publication deadline.
- Vexy utilizes a double-extortion RaaS model targeting mid-market and commercial enterprises across Latin America and North America.
- Defenders must focus on credential hardening, outbound exfiltration monitoring, and perimeter attack surface reduction.
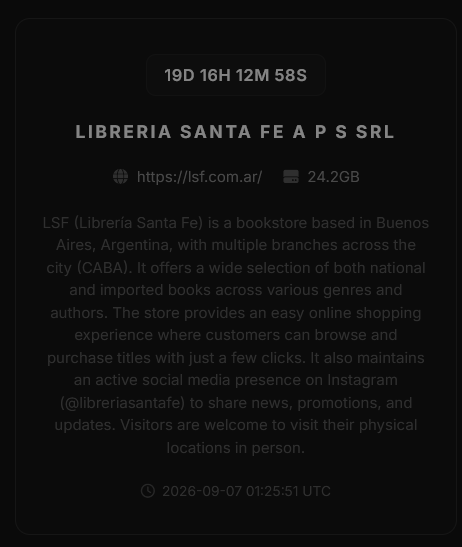
Staging 24.2 gigabytes of exfiltrated corporate records on a dedicated Tor-based leak portal, the emerging Vexy ransomware operation has issued a public extortion ultimatum against Argentinian bookstore chain Librería Santa Fe A.P.S. S.R.L. (lsf.com.ar). The threat actor announced the breach on September 7, 2026, establishing a 19 to 20-day countdown timer before releasing the full archive to underground repositories. This campaign highlights the growing focus of opportunistic ransomware syndicates on regional commercial entities possessing valuable point-of-sale configurations, enterprise databases, and customer records.
Incident Scope & Impact Metrics
What Happened in the Librería Santa Fe Incident
The security incident surfaced when operators behind the Vexy ransomware operation added Librería Santa Fe A.P.S. S.R.L. to their dark web leak directory at vexytsr3chimdz6siwaqi2lvxxwfkxvffkpwyanr2llequ2hkm56jvqd.onion. The group published metadata confirming the theft of 24.2 GB of internal organizational data, asserting that full unencrypted archives will be exposed if financial ransom negotiations are not initiated within the designated timeframe.
As an established commercial retail and bookstore network operating across Argentina, the target organization maintains sensitive supply chain, inventory, and customer databases. Threat actors leverage the exposure of this operational data to exert coercive pressure, attempting to bypass standard backup recovery defenses by relying on pure data theft and extortion.
Free exposure check
Dark Web Scanner
check dark web mentions, compromised account indicators, malware log signals, public breach exposure, and recent underground market activity for your domain.
Retail Blast Radius & Exposed Assets
- Point-of-Sale (POS) Recordshigh
- Customer & Billing Databaseshigh
- Supply Chain & Inventory Datamedium
- Proprietary Business Documentsmedium
How the Ransomware Operates Across the Attack Chain
Vexy operates under a double-extortion Ransomware-as-a-Service (RaaS) framework. While specific binary payloads can vary between individual affiliates, analysis of Vexy intrusions reveals a structured multi-stage intrusion lifecycle designed to maximize enterprise leverage before any encryption or public disclosure takes place.
Phase 1: Initial Access and Ingress
Affiliates targeting retail environments frequently acquire initial foothold access through stolen legitimate credentials sourced from infostealer botnet logs, credential-stuffing campaigns, or targeted phishing lures. In other observed deployments, threat actors target exposed perimeter interfaces, such as unpatched remote management portals, Virtual Private Networks (VPNs), or misconfigured remote desktop services.
Valid Accounts (MITRE ATT&CK T1078): Adversaries leverage compromised administrative or vendor credentials to authenticate directly against external gateways without triggering brute-force alerts.
Exploit Public-Facing Application (MITRE ATT&CK T1190): Exploitation of edge appliances with unmanaged software flaws facilitates remote code execution or internal routing bypasses.
Spear-Phishing (MITRE ATT&CK T1566): Delivery of malicious email attachments or links designed to execute lightweight downloaders or harvest employee tokens.
Phase 2: Internal Discovery and Lateral Movement
Once perimeter access is established, the adversary initiates stealthy discovery routines to identify domain architecture, active directories, and central file repositories. Rather than immediately deploying destructive payloads, the operators focus on locating structured databases, accounting systems, Point-of-Sale (POS) backend management servers, and proprietary internal documentation.
Adversaries often execute native administrative utilities (Living-off-the-Land techniques) such as nltest, net view, and PowerShell scripts to map domain trusts, locate accessible network shares (Server Message Block / SMB), and identify privileged administrator service accounts.
Phase 3: Data Staging and Exfiltration
Before initiating extortion demands, the threat actor aggregates target data into centralized, encrypted archives. In this campaign, 24.2 GB of structured files were staged and exfiltrated to external command-and-control (C2) nodes or public cloud storage repositories using tools like Rclone, MegaSync, or customized PowerShell file transfer scripts (MITRE ATT&CK T1048 and T1567).
Phase 4: Impact and Tor Extortion
Following successful transfer, the threat group lists the victim on their hidden Tor directory, establishing an extortion window of 19 to 20 days. Communication and payment negotiations are routed via Tor portals and Tox chat infrastructure, applying public reputational pressure to compel financial settlement.
Observed Vexy Intrusion Lifecycle
- 1Initial Ingress
Valid credentials, edge flaws, or phishing
- 2Discovery & Movement
AD, file shares, and POS server mapping
- 3Data Staging
24.2 GB compressed and staged for transfer
- 4Tor Extortion
Tor leak listing with 19-20 day ransom timer
Who Is Behind the Vexy Threat Group
Vexy represents an aggressive ransomware syndicate that gained operational momentum in early September 2026. The group utilizes a Ransomware-as-a-Service model, recruiting independent affiliates who carry out network intrusion and data exfiltration while the core team manages the Tor leak infrastructure, negotiation platforms, and revenue distribution.
Unlike threat actors dedicated solely to large global conglomerates, Vexy actively targets mid-market commercial enterprises, retail operators, and regional services across Latin America (including Argentina, Brazil, and Ecuador), North America, and parts of South Asia. By targeting organizations with lean internal defensive teams, the syndicate seeks rapid financial settlements from businesses looking to avoid regulatory scrutiny and customer trust erosion.
Observed Indicators of Compromise (IoCs)
Extortion Leak Portal:
vexytsr3chimdz6siwaqi2lvxxwfkxvffkpwyanr2llequ2hkm56jvqd.onionAdversary Negotiation Contact (Tox ID):
C32355C829A3CC4B320D4E78634FB4113B4B2918B383BB7AEAA48BDAAA4A0146E99B45A2A4C9
Enterprise Impact and Extortion Pressure on Retail Operations
The compromise of retail infrastructure introduces acute operational and legal risks. The exfiltration of 24.2 GB of proprietary data creates several critical business exposures:
Payment and Customer Data Exposure: Commercial retailers handle point-of-sale records, customer profiles, billing addresses, and payment transaction logs that carry severe liability if published on dark web forums.
Supply Chain and Commercial Disruption: Published vendor agreements, pricing models, inventory manifests, and internal communications compromise strategic positioning and partner trust.
Regulatory and Compliance Penalties: Failure to safeguard personal data can trigger regulatory investigations and financial sanctions under regional data protection frameworks.
Double-Extortion Leverage: Even if an enterprise maintains isolated offline backups to restore operational uptime, exfiltration-based extortion removes the safety net of simple disaster recovery.
Proactively evaluating edge systems through rigorous Penetration Testing and continuous Attack Surface Management enables organizations to discover and close perimeter gaps before ransomware operators identify them.
Adversary ATT&CK Mapping
Detection and Containment Guidance for Defenders
Security teams defending mid-market and enterprise retail environments must deploy multi-layered detection strategies focused on early-stage lateral movement, anomalous network egress, and compromised identity validation.
1. Network and Exfiltration Detection
Security Operations Center (SOC) teams should implement strict telemetry monitoring for abnormal outbound data flows:
Configure network perimeter sensors (Zeek, NetFlow, or next-generation firewalls) to flag sustained outbound data transfers exceeding 1 GB to unrecognized external IP addresses or public cloud providers.
Alert on direct outbound connections originating from internal servers toward known Tor exit nodes, anonymous proxy services, or unapproved VPN gateways.
Block outbound communication to uncommon file synchronization platforms across all server enclaves.
2. Identity Validation and Access Hardening
Because threat actors rely heavily on stolen credentials, identity verification is the primary defense layer:
Enforce phishing-resistant Multi-Factor Authentication (MFA) across all remote access vectors, administrative consoles, and remote desktop services.
Enable automated alerts for impossible travel, concurrent sessions from disparate geographical locations, or logins originating from commercial anonymizer ranges.
Enforce least-privilege role-based access control (RBAC) across shared file drives, limiting read/write access to sensitive directories containing proprietary commercial data.
3. Incident Response and Immediate Containment Steps
If an intrusion or data staging activity is suspected within the environment, incident responders should execute the following containment procedure:
Isolate Suspect Endpoints: Segregate affected application servers, database instances, and POS management hosts from the broader corporate network via host-based firewalls or VLAN quarantine.
Revoke Sessions and Reset Credentials: Perform a synchronized global password reset for all enterprise accounts, invalidating active Kerberos tickets, VPN sessions, and cloud access tokens.
Preserve Forensic Evidence: Capture memory dumps, triage system event logs (Security.evtx, System.evtx, PowerShell operational logs), and retain firewall telemetry dating back at least 30 days to isolate the initial entry point.
Monitor Identity Feeds: Leverage ongoing Dark Web Monitoring to detect if enterprise credentials or initial access tokens are circulating in underground broker markets.
How to Defend Against Similar Threats
- Implement phishing-resistant Multi-Factor Authentication (MFA) across all external access portals and VPN interfaces.
- Deploy network monitoring rules to detect and alert on anomalous bulk outbound data transfers exceeding 1 GB.
- Conduct regular penetration testing to identify unpatched edge devices and credential vulnerabilities before attackers exploit them.
- Restrict internal file share permissions to enforce the principle of least privilege across sensitive business data repositories.
Threat Intel FAQ
What is the Vexy ransomware group?
What data was stolen in the Librería Santa Fe security incident?
How can retail organizations protect against Vexy ransomware attacks?
Could a similar threat affect your organization?
If your team may be exposed to a similar threat, FemtoSec can help validate blast radius, prioritize remediation, and connect the issue to a practical security program.
Related Threats
October 16, 2026
Play Ransomware Targets The Innovation Group
Play ransomware operators have targeted United States management consulting firm The Innovation Group, publishing claims on their dark web leak site with a four to five day deadline to release stolen corporate data.
October 5, 2026
Panzer Ransomware Targets Healthcare with 33GB Exfiltration
Panzer ransomware has targeted UK healthcare provider SMCare, exfiltrating 33GB of sensitive organizational data. The double-extortion campaign leverages cross-platform payloads capable of targeting Windows and VMware ESXi environments, enforcing strict countdown timers on dedicated Tor leak sites.
October 5, 2026
Spirals Ransomware Hits Seven Seas Group in GCC
Spirals ransomware has claimed the compromise of GCC-based maritime services provider Seven Seas Group, demanding ransom under a strict data leak countdown. This incident underscores critical risks across regional logistics and transportation infrastructure.